ISO/IEC 27090:2026 – Detecting & Mitigating AI-Specific Security Risks
Event Date
November 23, 2026
Event Time
10:00 AM PST
Event Description
Learn what the ISO/IEC 27090:2026 standard means for your organization and how to put its guidance on managing AI threats into practice.
Webinar overview:
AI systems bring security risks that traditional controls were never designed to catch, including data poisoning, model theft, adversarial inputs, and prompt injection. ISO/IEC 27090:2026 gives organizations clear guidance for identifying these AI-specific threats and responding to them across the full AI lifecycle.
This webinar explains what the standard means for your organization and how to put its guidance into practice.
You will leave this webinar with the necessary knowledge to brief your leadership with confidence, close critical security gaps, and show regulators and stakeholders that your organization takes AI security seriously.
Course level: Basic to Intermediate.
Learning objectives:
- Know the AI threat landscape: Learn how AI-specific attacks such as data poisoning, evasion, model extraction, and membership inference differ from conventional cybersecurity threats.
- Apply ISO/IEC 27090:2026 in practice: See how the standard’s guidance turns into concrete actions for detecting and mitigating risks in AI systems.
- Secure the full AI lifecycle: Find the key points of exposure in data collection, model training, deployment, and ongoing operation.
- Strengthen your risk management: Bring AI-specific threats into your existing risk assessment and treatment processes, including frameworks built on ISO/IEC 27001 and ISO/IEC 42001.
- Build stronger AI governance: Set up the oversight, accountability, and monitoring needed to keep AI systems secure and trustworthy.
- Prepare for audits and regulators: Create the documentation and evidence that show due diligence to auditors, regulators, and stakeholders.
Areas covered:
- Introduction to AI Governance
- Understanding ISO/IEC 42001
- Understanding the NIST AI Risk Management Framework
- AI Risk Identification
- Building Trustworthy AI
- AI Governance Program Implementation
- Preparing for AI Compliance
Why should you attend?
AI adoption is moving faster than most security programs can adapt, and attackers are already targeting the gaps. Whether you are a compliance officer, AI governance professional, cybersecurity leader, or risk manager, you are expected to protect systems that behave in new and often unpredictable ways.
This session gives you a practical, standards-based roadmap for spotting AI-specific threats before they become incidents. You will leave with the knowledge required to brief your leadership with confidence, close critical security gaps, and show regulators and stakeholders that your organization takes AI security seriously.
Don’t wait for a breach to expose what your current controls miss.
Who will benefit:
- Chief Compliance Officers
- Chief Risk Officers
- AI Governance Professionals
- AI Ethics Committees
- Information Security Managers
- ISO 27001 Professionals
- Internal Auditors
- Risk Managers
- IT Managers
- Data Protection Officers (DPOs)
- Privacy Professionals
- Cybersecurity Professionals
- Legal Counsel
- Corporate Governance Professionals
- AI Project Managers
- Machine Learning Teams
- Technology Executives
- Digital Transformation Leaders
- Consultants responsible for AI governance
About the Instructor:
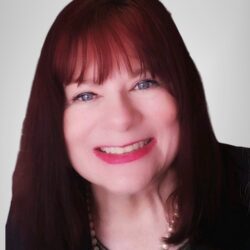
Dr. Michael C. Redmond, PhD., MBA
Dr. Redmond is an International Consultant, Auditor, Speaker, Author, and Trainer with more than 15 years of experience in regulatory compliance and the protection of sensitive information.
Dr. Michael C. Redmond has helped organizations create great AI governance, compliance, and trustworthiness programs. Her vast background includes consulting as a Sr. Manager for both Deloitte and KPMG for 7 ½ years, Chubb Services for 5 years, and 11 years with Redmond Worldwide.
Michael translates complex requirements into practical, actionable guidance on AI governance, AI risk management, and AI GRC audit readiness, consulting in Cybersecurity, Business Continuity Management, Emergency Management, and Incident Response.
Michael’s been honored as Top Woman in her field at a White House Luncheon and was selected out of the world to write the prologue for the chapter on RISK Management by the United Nations for their Disaster Management Book, which was given to the head of state for every UN member nation. She has been named on the list of “Women of Distinction for 2016” by Women of Distinction Magazine for her work in Cyber Security.
Refund Policy:
Attendees may cancel anytime before the webinar, and the refund will be processed within two working days of receiving the cancellation request. Requests for refund should be sent to care@thecomplyguide.com
We will process/provide a full refund if the webinar is canceled. The webinar may be canceled due to lack of enrollment or other unavoidable factors. Attendees will be notified 24 hours in advance if a cancellation occurs.
Participants who register but are unable to attend the webinar will also be provided a refund. On-demand recordings can be requested in exchange too.
Attendees who are not satisfied with the webinar content or quality can request a refund within 24 hours of the completion of the webinar. Refunds will be processed within 48 hours; no questions will be asked.
If you have any questions, please get in touch with us at care@thecomplyguide.com
Alternatively, you can register here